On‑device anonymization and PII masking
The Trackingplan SDK inspects only the requests client sites or apps already sends to third‑party services, processes them locally, and forwards to our backend only the events—already anonymized—needed for anomaly detection.
- Local request inspection: The SDK only observes network requests already being sent to third-party vendors you've explicitly declared (like Google Analytics or Meta).
- In-browser/app processing: All data parsing, anonymization, and masking happens directly on the user's device—before anything is sent to Trackingplan's servers.
- Configurable PII rules: Define your own filters using flexible regex patterns or vendor-specific presets to detect and scrub sensitive data in real time.
Automated Alerts for Sensitive Data Breaches
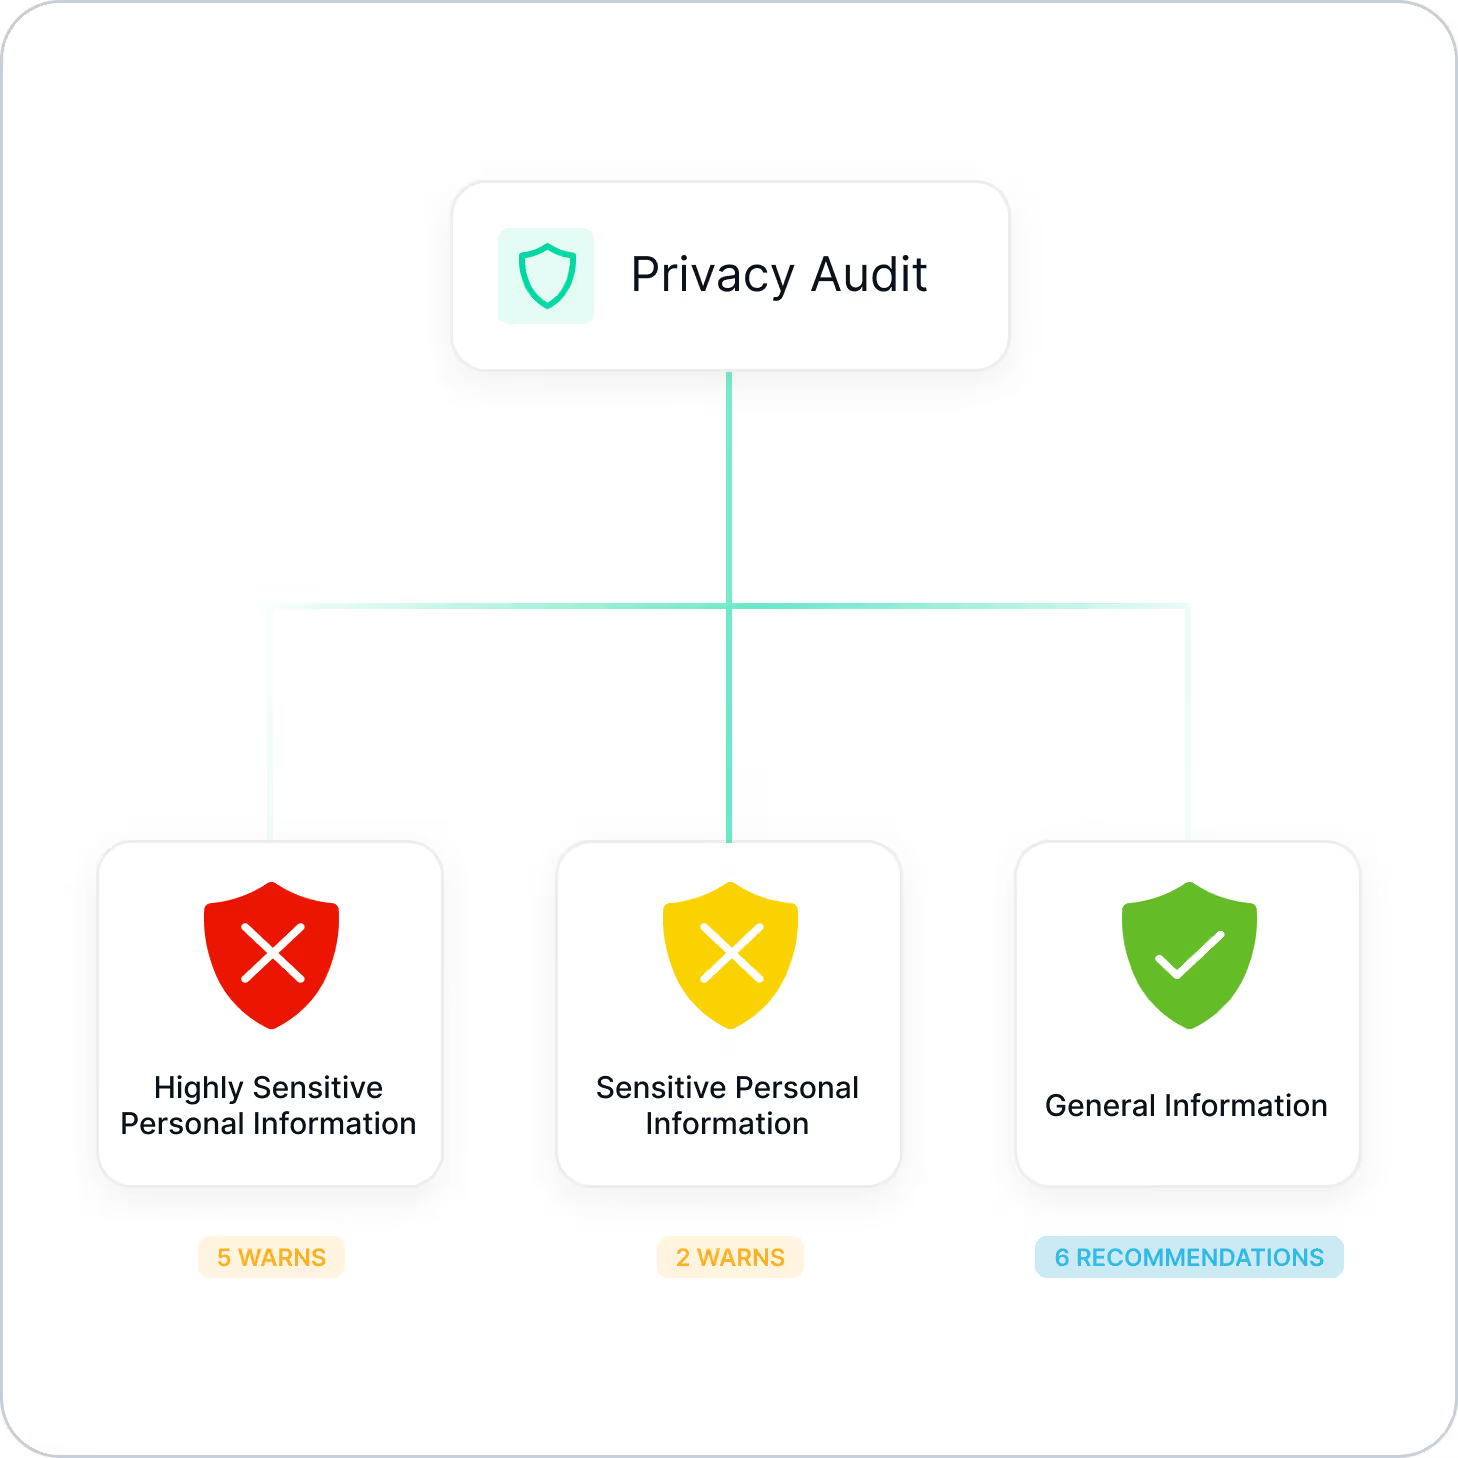
Trackingplan helps you stay ahead of accidental data leaks and PII exposure with continuous monitoring and instant alerts.
- Privacy Audit: Automatically monitors your sites and apps for accidental private‑data leaks to other vendors.
- Consent Validation: Verify that no data is sent when users opt out via Consent Mode and be alerted whenever a vendor receives data that contravenes user choice.
Privacy comes first
Trackingplan does not store anything until anonymization measures are applied.
- Encrypted and isolated by default: All data is encrypted in transit (TLS 1.2+) and at rest (AES‑256) and stored in hardened AWS services with fine-grained access controls.
- No storage of personal data: Customer data is isolated per environment, not linked across clients, and is automatically destroyed after 90 days.
- Built-in security practices: CI/CD deployments, peer-reviewed code, 2FA, audit logs, and 24/7 on-call monitoring are standard.
LEGAL VALIDATION
Trusted by Privacy-Conscious Companies
Trackingplan successfully works with privacy-conscious companies, including renowned brands and neobanks, who have received legal validation for our extensive security practices.
Your data privacy questions answered
?Do you collect any data about my users?
The Trackingplan SDK only inspects the network requests that your site or app already sends to third‑party vendors (e.g., Google Analytics, HubSpot, Mixpanel, Google Ads), and forwards to our backend only the events required for anomaly detection, already anonymized on-device.
These requests are parsed locally in the browser or app, where anonymization and masking are applied as configured. Only the processed, non-identifiable event data is transmitted to Trackingplan’s servers. Once received, events are parsed, modeled, and continuously monitored to detect anomalies that may indicate implementation issues, whether in your own tracking or introduced by third-party tools. Through our web interface, teams can explore the detected schema, review alerts, and inspect sample events to debug tracking errors with full visibility and control.
Additionally, we do not introduce new identifiers, nor store IP addresses or fingerprinting data, as these are stripped before processing.
For a complete overview of our privacy and security measures, please visit our Privacy & Security documentation.
?How does Trackingplan handle the data it receives when customers use Trackingplan?
At Trackingplan, we are committed to full transparency in how we handle data and protect user privacy. Our platform is designed with privacy, security, and compliance at its core, ensuring that our clients maintain complete control over their data while meeting the strictest privacy regulations.
The Trackingplan SDK only observes the network requests your site or app already sends to third-party services—such as Google Analytics, HubSpot, Mixpanel, or Google Ads. These requests are parsed locally within the user’s browser or mobile app, where any necessary anonymization or masking is applied according to your configuration. Only processed, anonymized events—never raw or identifiable data—are forwarded to Trackingplan’s backend, strictly for anomaly detection purposes.
Client data remains fully encrypted and logically isolated at all times. Our infrastructure runs on hardened AWS PaaS services, with encryption enforced both in transit and at rest. Fine-grained IAM roles and resource-level permissions ensure strict access control, while all customer data is automatically deleted after 90 days by default.
Security is not just technical—it’s built into our processes. Every code change is peer-reviewed and deployed via CI/CD pipelines. Our team enforces two-factor authentication (2FA), maintains detailed audit logs, and ensures 24/7 system monitoring with on-call coverage to guarantee availability. GDPR principles are embedded into our design, and we offer optional Data Processing Agreements (DPAs) to support legal and regulatory compliance.
Through Trackingplan’s web interface, clients can inspect data schemas, review alerts, and analyze sample events in real time—empowering teams to debug implementation issues and safeguard data quality, without ever compromising user privacy.
For a complete overview of our privacy and security measures, please visit our Privacy & Security documentation.
?Will the installation script interfere with my site or cause security issues?
No. The Trackingplan installation script is specifically engineered to be lightweight, non-intrusive, and secure—comparable to those used by trusted observability tools like Datadog and Sentry. At under 10KB, it loads asynchronously and does not block or delay the execution of any existing page elements or scripts.
The script is served directly as source code to eliminate the risk of unauthorized changes. It has been thoroughly reviewed by some of the most security-conscious clients in the industry, including data-driven organizations and privacy-focused teams. For companies that require additional assurance, we offer access to the decompiled version of the script under a signed non-disclosure agreement (NDA).
Designed with privacy and performance in mind, the script works only on declared endpoints—intercepting requests to third-party vendor domains that you’ve explicitly selected for monitoring. It performs anonymization and masking locally within the browser or app, without relying on external dependencies or introducing new cookies, storage mechanisms, or cross-site tracking.
Trackingplan's script never collects more data than your site or app already sends to analytics providers. It simply observes outgoing requests and ensures that only anonymized, relevant data needed for anomaly detection reaches our backend—without interfering with your application or compromising user privacy.
For a complete overview of our privacy and security measures, please visit our Privacy & Security documentation.
?Where are your servers located?
Trackingplan infrastructure runs exclusively on hardened cloud infrastructure in the EU — AWS (Frankfurt), ClickHouse Cloud (Frankfurt), Cloudflare's edge network, and Microsoft Azure for AI.
All customer data is processed and stored in the EU.
All endpoints are protected via AWS WAF, TLS 1.2+ encryption, and AES‑256 at rest.
For a complete overview of our privacy and security measures, please visit our Privacy & Security documentation.
?Does Trackingplan use cookies or user IDs?
No, Trackingplan does not store or collect any personal data.
We are fully committed to respecting user privacy and maintaining compliance with global privacy regulations such as GDPR and CCPA. Trackingplan only observes the data your site or app is already sending to analytics or marketing tools—and only for the purpose of monitoring tracking quality and detecting implementation issues.
Here’s how Trackingplan handles identifiers and user data:
- Cookies: Trackingplan does not use cookies. Our SDK only uses local storage to keep it working locally, but never to identify users across different sessions or transmits that information to their servers.
- User IDs: If your site or app sends user IDs to your analytics or ad vendors, Trackingplan will inspect these requests as part of its monitoring. However, these IDs are never stored, linked, or enriched with additional information. All data is anonymized or masked on the user’s device before being forwarded for analysis.
- Fingerprinting: Trackingplan does not use any form of fingerprinting. We do not collect device characteristics, behavioral patterns, or any other data used to generate unique identifiers.
In short: Trackingplan never introduces new tracking mechanisms, never stores personal data, and never builds user profiles. We act only as a passive observer of the data you're already sending to your vendors, with strict safeguards in place to prevent access to personally identifiable information (PII).
If you have questions about how Trackingplan handles data privacy or want to review the decompiled script under NDA, please contact our support team. For a complete overview of our privacy and security measures, please visit our Privacy & Security documentation.